Access Explorer
See exactly what every user can read, write, create and delete across every model, resolved through group inheritance and record rules
The video below shows Access Explorer running on a real Odoo 19 database. Want it driven against your own data, or a question answered first? Ask and we will set up a session.
What it does
The dangerous permission is the one nobody thought to check
Checking access user by user only finds what you already suspected. It cannot find the access rule someone left without a group on it, which quietly grants every user in the database. It cannot tell you which of your models nothing narrows, so that access to the model is access to every row. And it will not tell you who can delete accounting entries until you think to ask about that particular person and that particular model.
This sweeps every user against every model that matters and tells you what stood out.
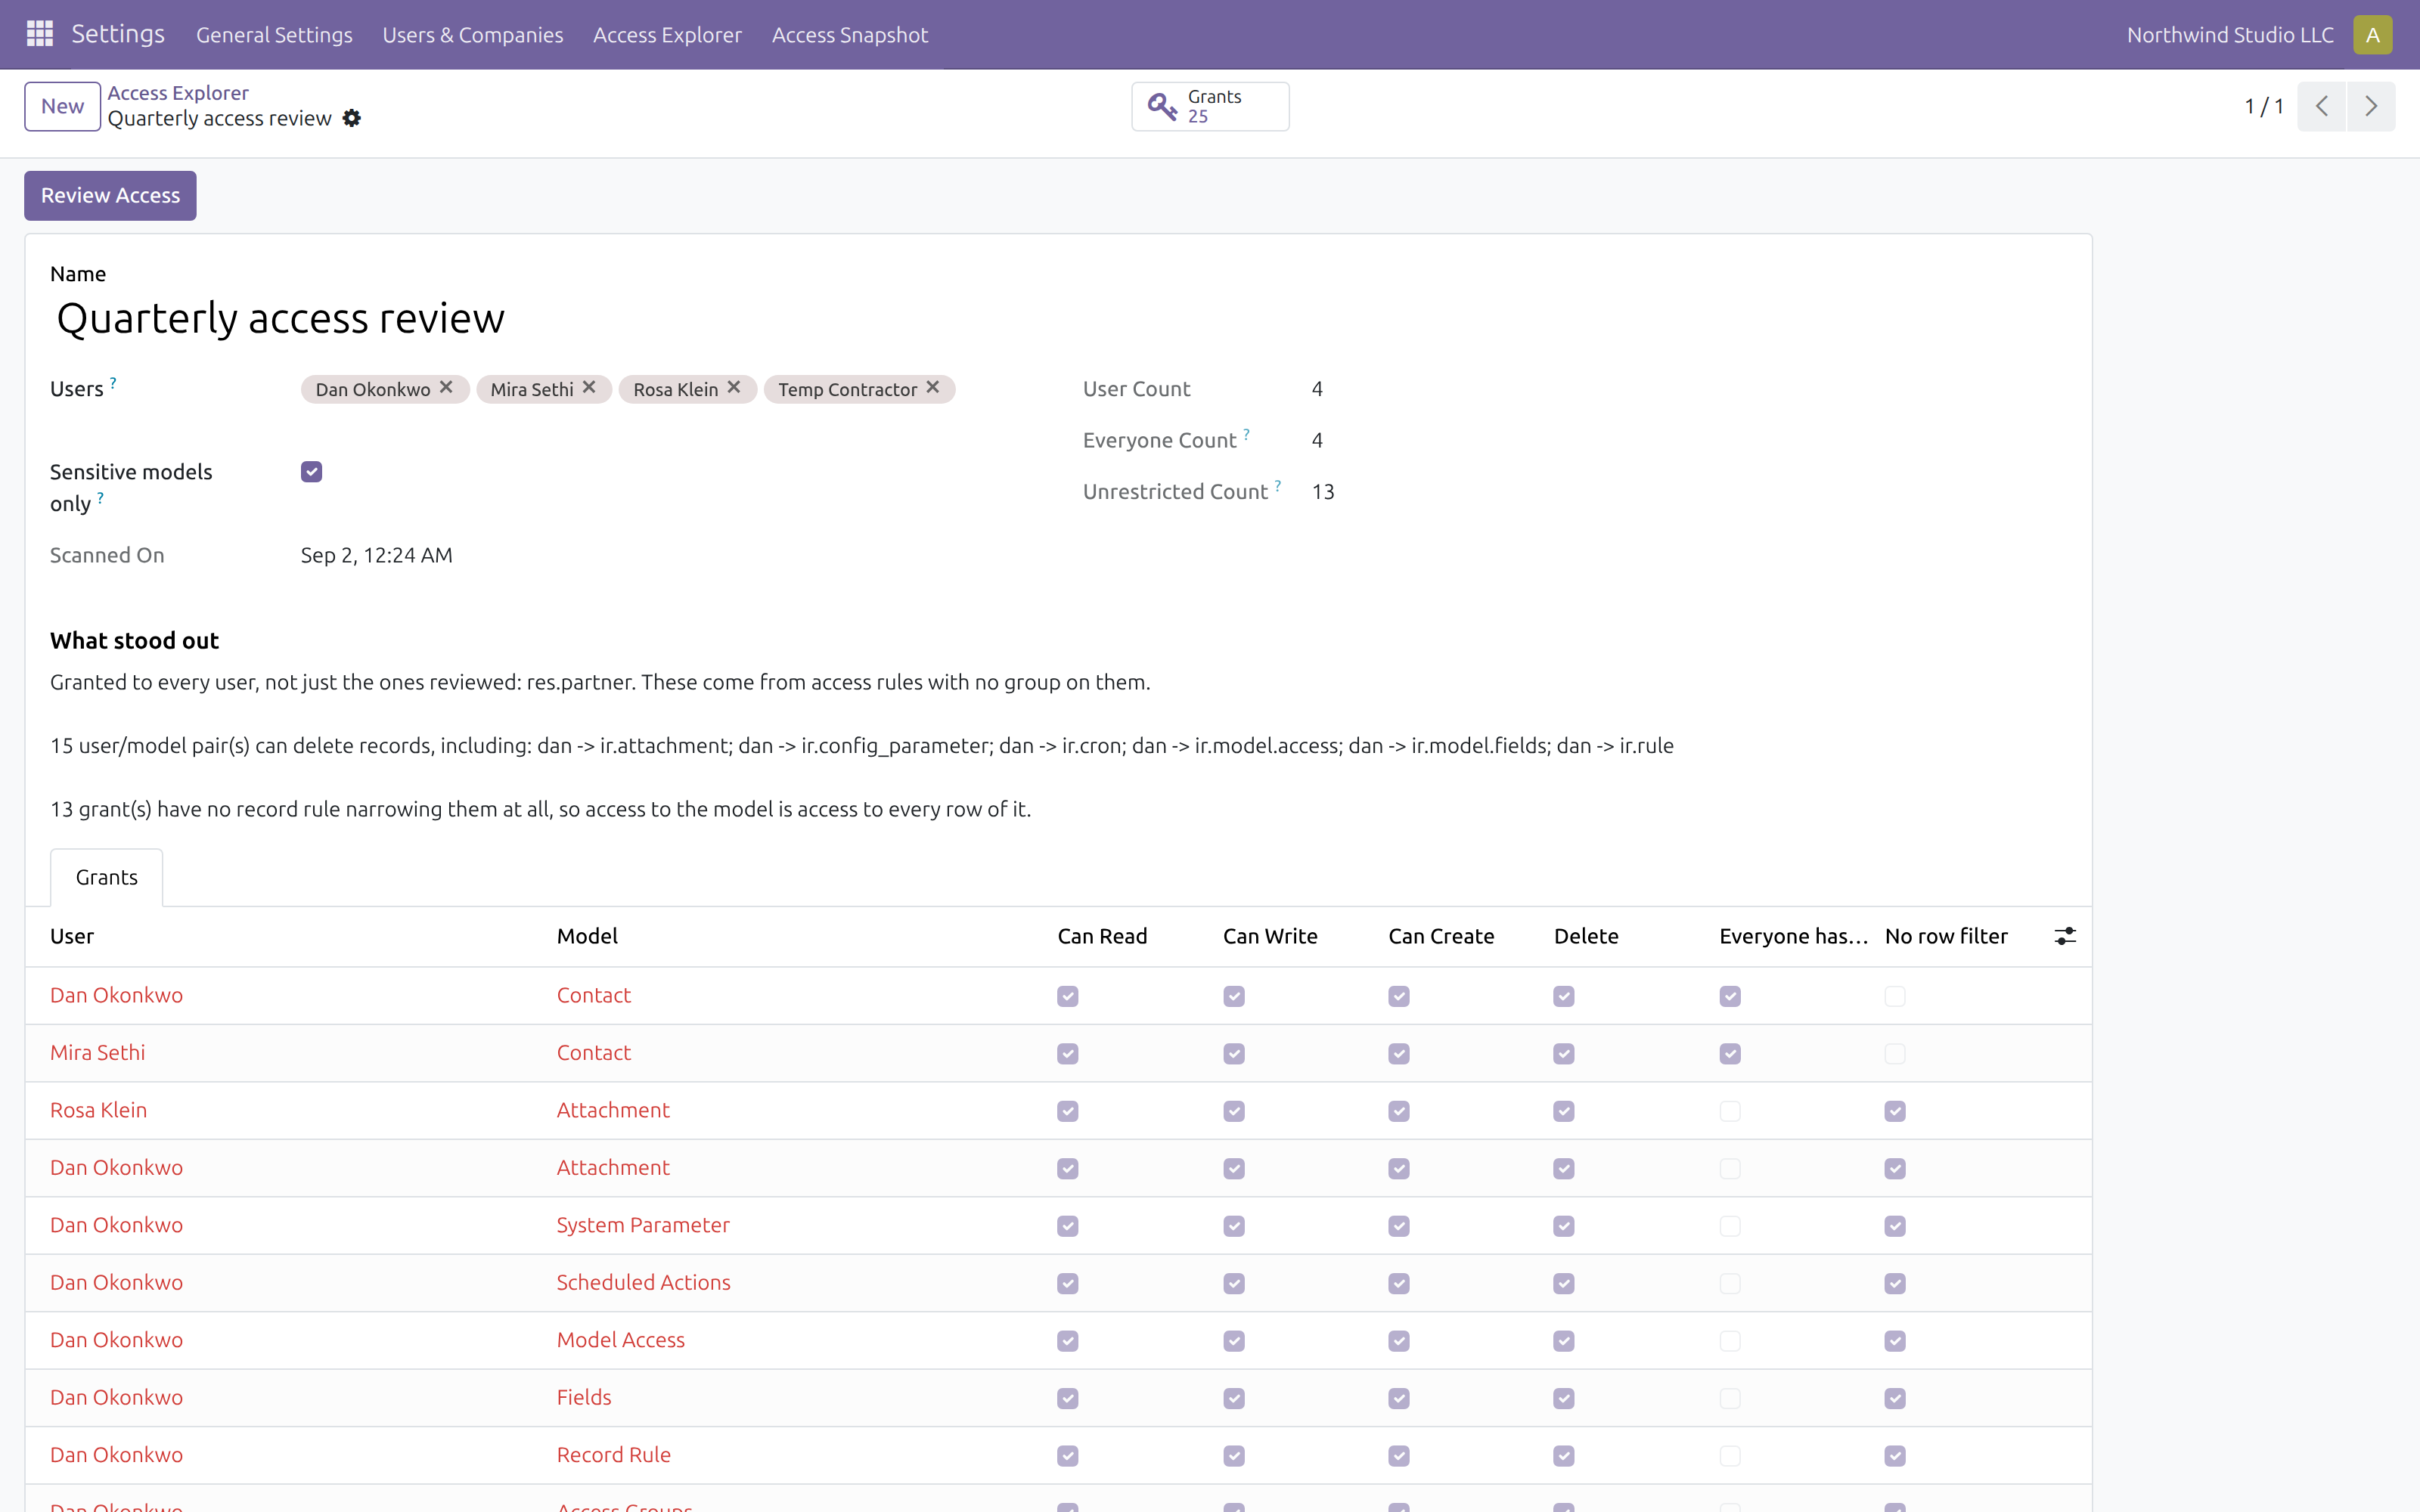
A review across users and sensitive models: what each can do, which grants reach everyone, and which are narrowed by no record rule at all.
Grants that reach everyone
An access rule with no group on it applies to every user in the database. It is the most common accidental over-grant in Odoo and the hardest to notice, because checking any single user shows nothing unusual - they are supposed to have it. The review flags every one of them by name.
Access with no row filter
A grant that no record rule narrows means access to the model is access to every record in it. That is often correct and occasionally alarming, and you cannot tell which without being shown where it happens.
Resolved, not listed
Permissions are computed as each user, through the same calls Odoo uses to enforce them - so implied groups, global rules and group rules are already combined. You are reading a conclusion, not three tables to cross-reference.
The superuser is left out on purpose
It bypasses every rule by design, so including it would report full access to everything and bury the findings that matter. It is excluded even if you select it.
What it does not do
Stated up front so nothing about the scope is a surprise after you buy it.
Screenshots
Requirements
- Odoo 19.0, Community or Enterprise.
- Odoo.sh or On-Premise only. Third-party apps cannot be installed on Odoo Online (SaaS) databases — check your hosting before buying.
- Odoo 19 Community or Enterprise. No dependency beyond base, and nothing leaves your server. Restricted to Settings administrators, since the report itself describes who can reach what.
- Module
mh_access_explorer, version 19.0.1.0.11, licensed OPL-1.
Related apps
Eleven access tools in one app, from who-can-do-what across every model to safe offboarding
Set the default list view columns for a model and assign them per group, so a team opens the same layout instead of rebuilding it
MCP server exposing Odoo to Codex and other MCP clients - on the current 2026-07-28 revision, with an explicit list of what each connection may reach